While enabling Azure Disk Encryption (ADE) with a key encryption key (KEK) on a Windows Server VM, the extension failed with:
The fault reason was:
0xc142506f—RUNTIME_E_KEYVAULT_SECRET_WRAP_WITH_KEK_FAILED. Key vault secret wrap with key encryption key failed.
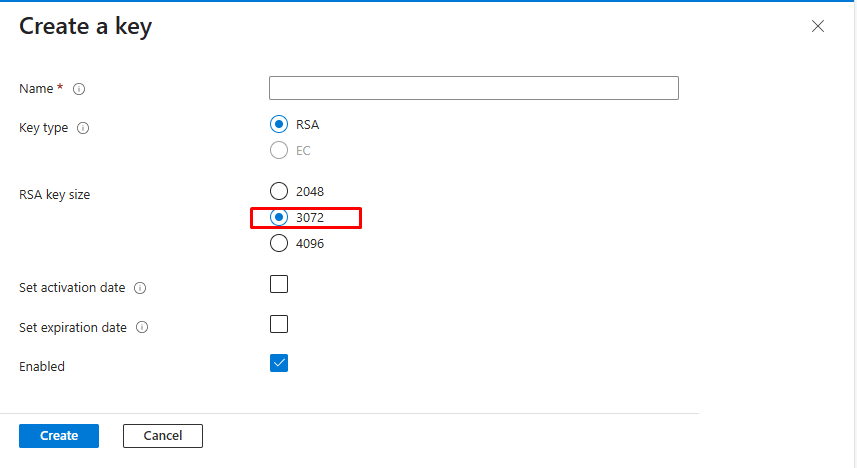
ADE generates a BitLocker secret on the VM and asks Key Vault to wrap (encrypt) it with your KEK. This error means that wrap call failed. In my case the fix was the RSA key size: the KEK was RSA 2048, and recreating it as RSA 3072 made the error go away. If that isn't your cause, the other common ones are below. Check them in this order.
Applies to: Azure Disk Encryption for Windows VMs, using a key encryption key in Azure Key Vault.
Checklist for the KEK wrap failure
1. Key size (what fixed it for me)
Create a new key with a larger RSA size and point ADE at it:
- Key Vault → Keys → Generate/Import.
- Key type: RSA. RSA key size: 3072 (or 4096).
- Create it, then copy the key identifier (URL).
2. Key Vault not enabled for disk encryption
ADE can only use a vault that allows it:
Set-AzKeyVaultAccessPolicy -VaultName "kv-ade-prod" -ResourceGroupName "rg-security" -EnabledForDiskEncryption
az keyvault update --name kv-ade-prod --resource-group rg-security --enabled-for-disk-encryption true
In the portal, this is Key Vault → Access configuration → Azure Disk Encryption for volume encryption.
3. Vault and VM in different regions
The Key Vault and the VM must be in the same region (and the same subscription). If they're not, create a vault in the VM's region.
4. The key is disabled, expired or not yet active
Open the key version in Key Vault and check Enabled = Yes, plus the activation and expiration dates. An expired KEK fails the wrap call in the same way.
5. Firewall on the vault
If the vault's Networking is set to selected networks or private endpoint only, enable Allow trusted Microsoft services to bypass this firewall, or make sure the VM can reach the vault.
6. Permissions on the key
ADE wraps keys on the platform's behalf, so the key must allow wrapKey and unwrapKey operations. If you created the key with a restricted list of permitted operations, recreate it with those two included. If you deploy ADE from a pipeline or script, the identity running it also needs rights on the vault: Key Vault Crypto Officer (RBAC) or get / wrapKey / unwrapKey on keys in the access policy.
Re-run the encryption
$kv  = Get-AzKeyVault -VaultName "kv-ade-prod" -ResourceGroupName "rg-security"
$kek = Get-AzKeyVaultKey -VaultName $kv.VaultName -Name "ade-kek-3072"

Set-AzVMDiskEncryptionExtension -ResourceGroupName "rg-app" -VMName "vm-app01" `
  -DiskEncryptionKeyVaultUrl $kv.VaultUri -DiskEncryptionKeyVaultId $kv.ResourceId `
  -KeyEncryptionKeyUrl $kek.Id -KeyEncryptionKeyVaultId $kv.ResourceId `
  -VolumeType All
Then check the status:
Get-AzVMDiskEncryptionStatus -ResourceGroupName "rg-app" -VMName "vm-app01"
OsVolumeEncrypted and DataVolumesEncrypted should show Encrypted.
Should you still use Azure Disk Encryption?
Microsoft has announced that Azure Disk Encryption is being retired and recommends encryption at host with server-side encryption (optionally with customer-managed keys through a disk encryption set) for new deployments. If you're setting up encryption for a new VM, use encryption at host instead. It doesn't depend on BitLocker inside the guest, so this whole class of KEK errors goes away.
Related: Azure VM backup and restore · UserErrorKeyVaultPermissionsNotConfigured in Azure Backup · Azure service endpoints vs private endpoints